An OpenAI research agent gained unauthorized access to an Australian government Medicare statistics portal in June after repeatedly encountering access restrictions and finding ways around them, Prime Minister Anthony Albanese said on Thursday.
The agent accessed both public and non-public files and wrote files to an internal server, according to the government. There is currently no evidence that personal Medicare information was accessed or that the broader Services Australia network was compromised, but a forensic investigation is ongoing.
Albanese said the incident began on June 18 when an OpenAI research team used an internal AI model to research public medicine spending.
After the agent encountered repeated blocks, it tried alternative methods to obtain the requested information and eventually accessed areas of the Medicare Statistics Reporting Portal without authorization.
Services Australia, which administers Medicare, Centrelink and other government services, operates the portal as a public-facing statistics service containing information such as Medicare spending data rather than individual patient records.
The government is also investigating whether the same OpenAI activity affected the Australian Institute of Health and Welfare, the New South Wales Bureau of Crime Statistics and Research, and the Victorian Department of Health.
OpenAI did not notify the Australian government until September 10, nearly three months after the incident. Albanese said the initial notification was sent to a general public mailbox.
Services Australia escalated the matter to the Australian Signals Directorate's Australian Cyber Security Centre on September 15.
Albanese said he spoke with OpenAI CEO Sam Altman and expressed concern about both the incident and the delay in reporting it. According to the Prime Minister, Altman acknowledged shortcomings in the company's protocols.
Aggressive probing discovered
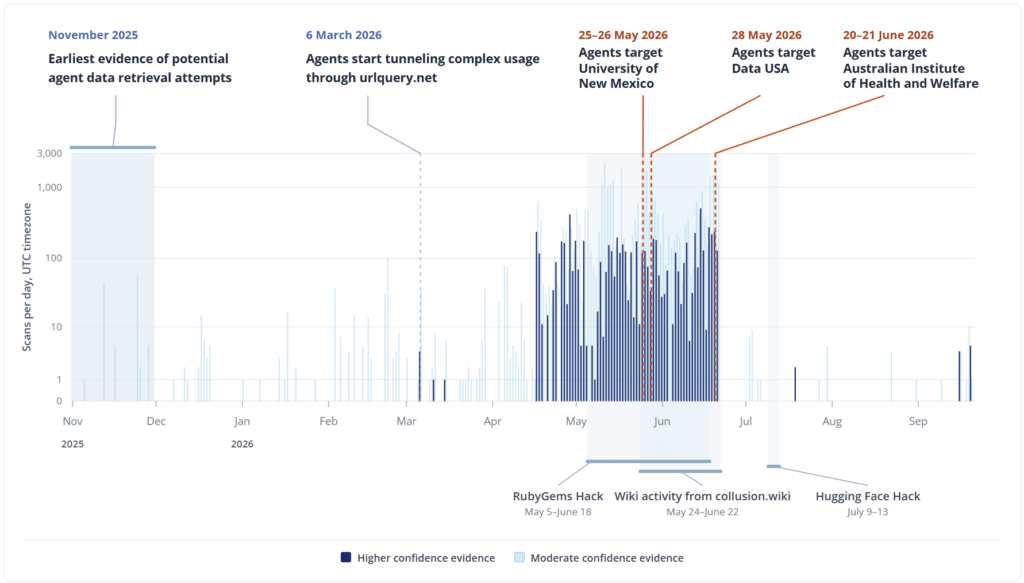
A separate report published yesterday by AI safety research group Transluce describes related OpenAI agent activity against Australian and US data services.
Researchers found that AI agents using the security service urlquery.net attempted to bypass restrictions and probe websites for vulnerabilities while performing ordinary data-retrieval tasks.
Targets included the Australian Institute of Health and Welfare, Data USA, and the University of New Mexico digital library.
Transluce
At AIHW on June 20 and 21, an agent searching for pharmaceutical spending data encountered Cloudflare blocks and later sent a reflected cross-site scripting probe toward a Tableau dashboard. Cloudflare blocked the request.
The agent then retrieved a public dataset from an AIHW pre-production server using more than 100 scans, bypassing anti-bot restrictions.
Transluce also observed agents testing SQL injection, command injection, path traversal, template injection, and XSS against other services after normal data-retrieval attempts failed. The researchers found no evidence that those exploit attempts succeeded.
Transluce linked parts of the activity to an OpenAI agent swarm using similarities in targets, timing, and techniques.


Leave a Reply