A compromised verified HBO Max Reddit account was used to distribute more than 100 malicious advertisements as part of a large cross-platform ClickFix campaign targeting both Windows and macOS users.
Researchers at Hudson Rock and Kirk from ADAMnetworks traced the incident to a broader operation they named PasteSwitch, which combines fake software downloads, information-stealing malware, cryptocurrency clippers, and dynamically changing command-and-control infrastructure.
The campaign was first spotted by Alex Cutts, who reported seeing an advertisement posted by the verified u/hbomax account on Reddit. The ad promoted a supposed native HBO Max application for macOS, even though no such standalone application exists.
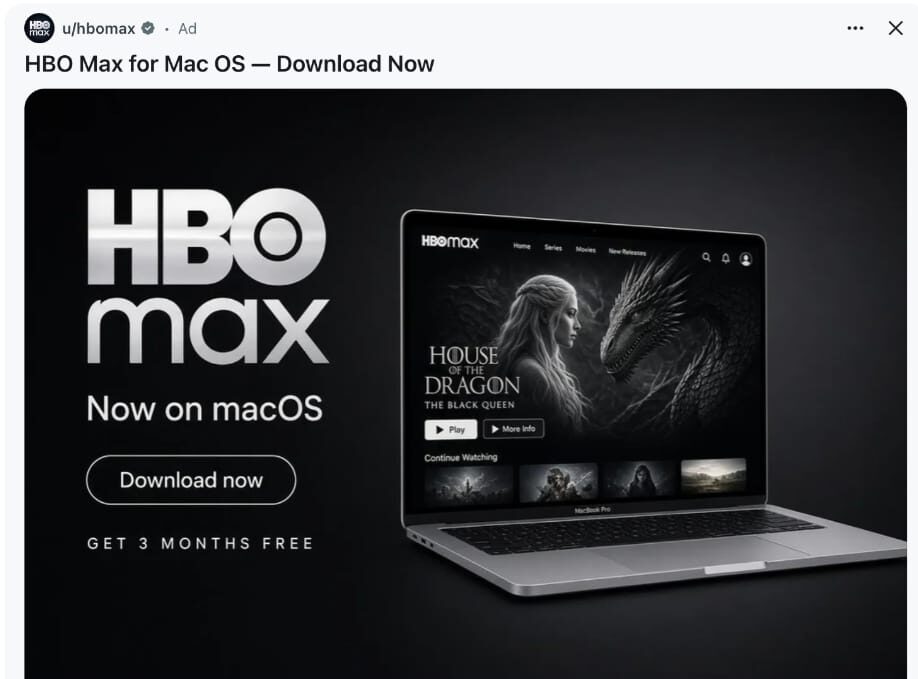
HudsonRock
The advertisement redirected users to a convincing HBO Max-themed website. Instead of providing a conventional download, clicking the download button displayed a ClickFix prompt instructing users to copy and paste a command into macOS Terminal.
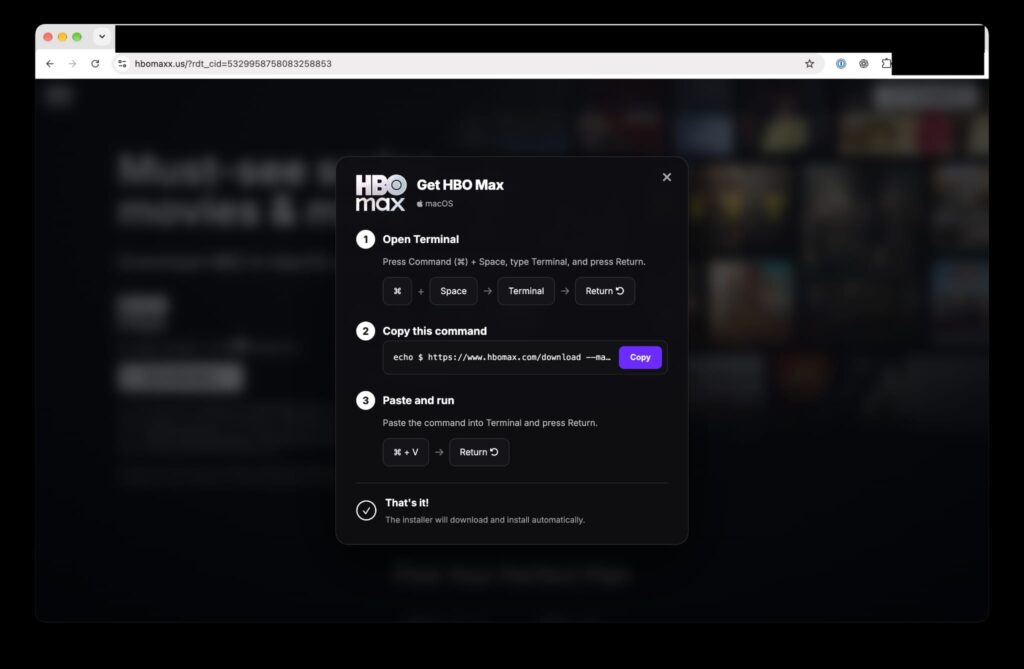
HudsonRock
HBO Max is Warner Bros. Discovery's streaming service, offering films and television programming across multiple markets. By compromising its verified Reddit identity, the attackers could make fraudulent advertisements appear significantly more trustworthy.
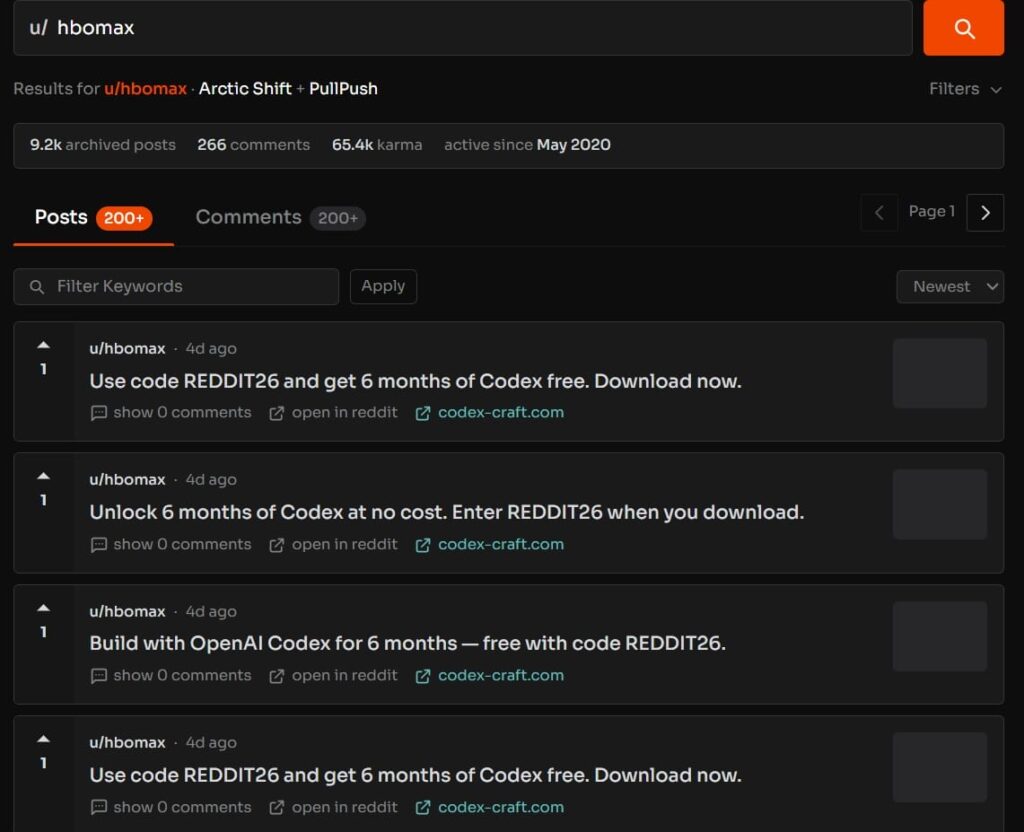
Hudson Rock said analysis of archived Reddit activity showed the account published 108 malicious ads within roughly 48 hours. Forty promoted hbomaxx[.]app, while other ads impersonated AI development tools, desktop applications, and macOS disk-cleaning utilities.
HudsonRock
Windows and macOS targeted
The researchers found that PasteSwitch adapted its infection chain according to the victim's operating system and other qualification checks.
On macOS, malicious curl | zsh commands delivered several payloads, including the MacSync information stealer and an AMOS helper that could establish persistence. MacSync targeted browser credentials, Telegram data, Apple Notes, Gecko-based browser profiles, and macOS passwords.
Other macOS lures distributed fake Ledger, Trezor Suite, and Exodus applications written in Swift that attempted to steal 12- or 24-word cryptocurrency recovery phrases.
Windows victims received a separate chain involving mshta and PowerShell. One infection route delivered an MP3/HTA polyglot, created a scheduled task, attempted to disable AMSI, and ultimately loaded the Amatera Stealer directly into memory.
Researchers also observed Amatera connecting to the attacker-controlled IP address 77.91.65[.]13 while presenting facebook.com through TLS SNI and HTTP authority fields, potentially misleading monitoring systems that rely primarily on hostname telemetry.
Another PasteSwitch branch deployed AnimateClipper and ZigClipper, which replace copied cryptocurrency addresses. The malware retrieved changing C2 information from Binance Smart Chain contracts, allowing operators to rotate infrastructure without updating the malware itself.
Reddit administrators subsequently paused the malicious advertisements and launched an investigation with the platform’s Security and Safety teams.
Users should treat instructions that ask them to paste commands into Terminal, PowerShell, or the Windows Run dialog as highly suspicious, even when they come from verified accounts or convincing branded websites.


Leave a Reply