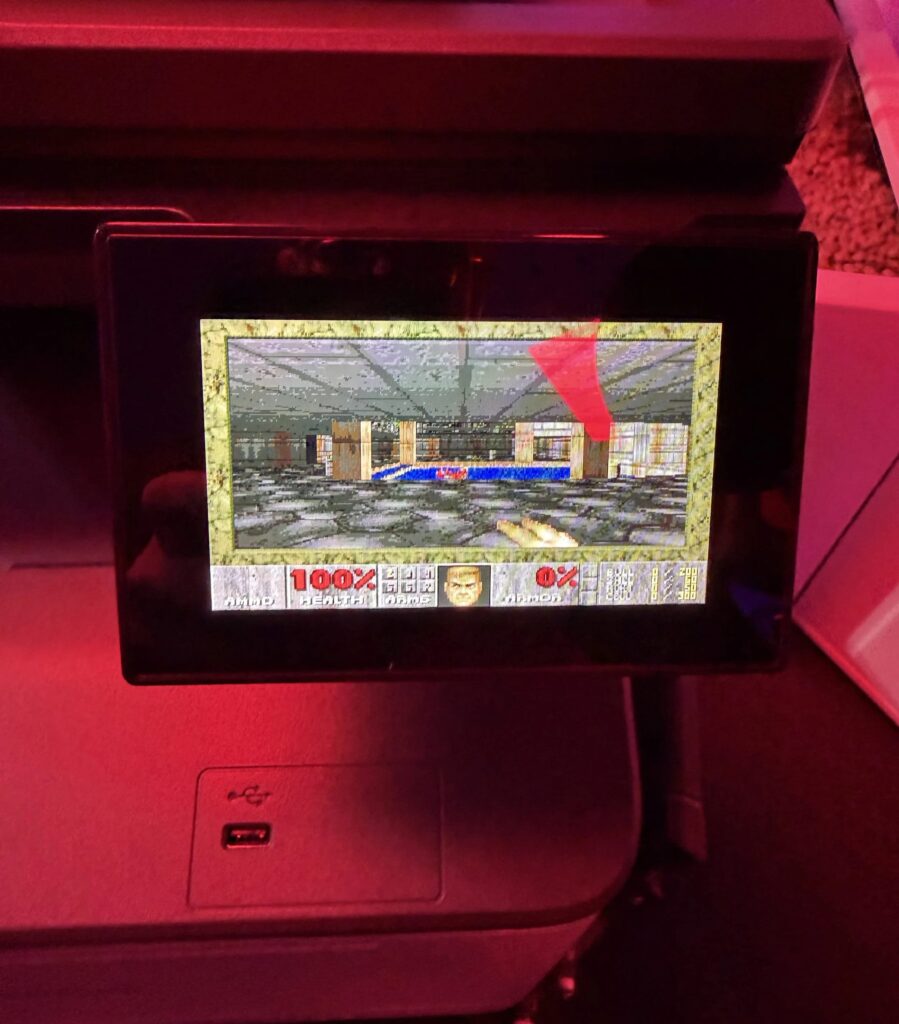
Interrupt Labs hacked a Lexmark CX532adwe printer and displayed DOOM on its screen during the second day of Pwn2Own Ireland 2026, earning $5,000 and two Master of Pwn points.
The October 7 session also saw successful attacks against Samsung’s Galaxy S26, Home Assistant Green, Sonos speakers, and AI infrastructure, bringing the competition’s current tally to $621,000 awarded for 77 unique zero-day vulnerabilities.
According to ZDI’s Day Two recap, the Lexmark demonstration was one of three successful attempts against the same printer model. A photograph accompanying the results shows the classic first-person shooter on the device’s display, although the announcement does not describe the vulnerabilities Interrupt Labs used.
Rick de Jager and Filippo Cremonese of Zellic/V12 Security also exploited the CX532adwe, collecting $5,000 and two points. BoredPentester earned another $4,250 with a three-bug chain comprising two unique vulnerabilities and one collision.
Collisions are vulnerabilities already known to the organizers or vendor, including bugs demonstrated by earlier contestants, which can reduce an entry’s payout.
Elsewhere in the printer category, McCaulay compromised the Canon imageFORCE 1643F using hard-coded credentials, missing authentication for a critical function, and command injection, earning $10,000. Team Confused’s attempt against the Brother MFC-L8970CDW was unsuccessful.
ZDI
Phones, smart homes, and AI targets
Samsung’s Galaxy S26 fell to three separate teams during the day.
Dimitrios Valsamaras, Ken Gannon using Djini.ai from Mobile Hacking Lab, and Tenia Valsamara of CENSUS Labs succeeded with a single confused-deputy vulnerability, a flaw that causes a privileged component to misuse its authority.
KAIST Hacking Lab’s Kyeongmin Kim remotely compromised the phone using one unique bug and two collisions, earning $8,500. PetoWorks also achieved remote access, but all three vulnerabilities in its chain were collisions, resulting in a $6,250 award.
Home Assistant Green repeatedly fell to multi-bug chains. McCaulay’s six-bug exploit contained five zero-days and one collision, while PetoWorks used three unique bugs and two collisions. Xint’s Yves Bieri earned $30,000 for another successful attack against the smart-home hub.
In AI infrastructure, HaeJung Yang of Out of Bounds received $40,000 for exploiting Dynamo, the largest individual payout explicitly listed in the Day Two recap.
Oracle Autonomous AI Database was compromised by Xint’s Taisic Yun using two zero-days and three collisions, and by Ikotas Labs using a seven-bug chain ending in use-after-free and type-confusion flaws. Team MAMMOTH also exploited Chroma with one zero-day and two collisions.
Other successful demonstrations targeted the Sonos Era 300 speaker and Garmin Index BPM blood-pressure monitor.
Xint leads the standings
The current leaderboard lists Xint first with 12.5 points and $90,000, followed by Ikotas Labs with the same points total and $61,000.
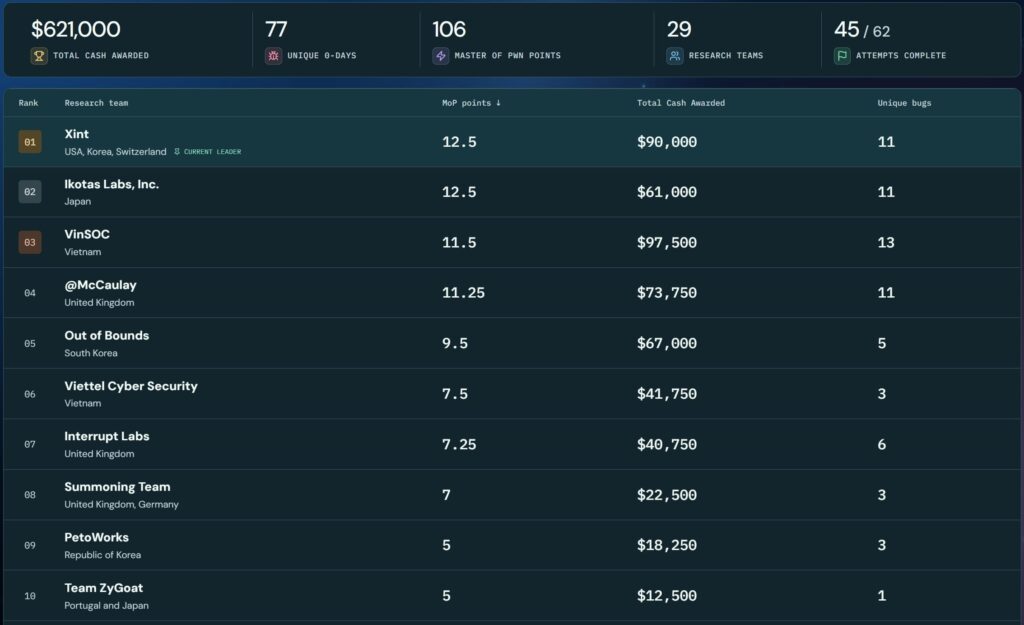
VinSOC ranks third with 11.5 points and $97,500, ahead of McCaulay’s 11.25 points and $73,750. Interrupt Labs sits seventh with 7.25 points and $40,750.
The leaderboard records 45 completed attempts out of 62, leaving 17 more demonstrations scheduled for Day 3, before the Master of Pwn is crowned.


Leave a Reply