Security researchers have successfully exploited Samsung’s Galaxy S26 three times during the opening day of Pwn2Own Ireland 2026.
The confirmed results published so far show 28 zero-days totaling $342,500 in awards, with several entries receiving reduced payouts because their exploit chains included previously known vulnerabilities.
The competition began on October 6 in Cork, Ireland. Organized by TrendAI’s Zero Day Initiative (ZDI), it attracted more than 60 entries, with attempts scheduled across three days and a record number of phone entries. The opening-day schedule also includes targets such as Google’s Pixel 10, Oracle Autonomous AI Database, and OpenAI Codex.
Pwn2Own rewards researchers for demonstrating working exploits against designated targets and disclosing the underlying vulnerabilities. This year's categories span mobile phones, smart home devices, wellness products, printers, messaging, AI infrastructure, and coding agents.
Galaxy S26 exploit chains
Nguyen Thanh Dat of Viettel Cyber Security exploited the Galaxy S26 using four bugs, three already known to Samsung, earning $31,250 and 3.25 Master of Pwn points.
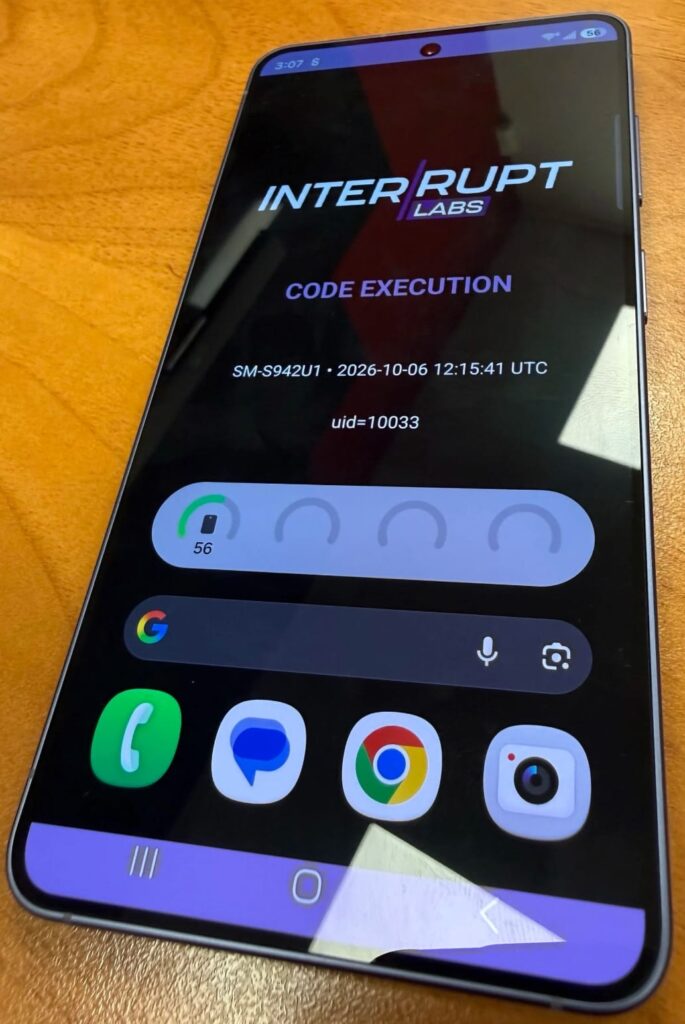
Interrupt Labs also used four bugs, including three collisions and one zero-day, earning $15,750 and 3.25 points.
A third successful Galaxy S26 attempt, by Ikotas Labs, combined four bugs. One was already known to the vendor but remained unpatched. The team received $11,000 and 4.5 points.
Under the contest rules, previously known vulnerabilities can qualify for reduced awards at the organizer’s discretion. A collision therefore does not necessarily mean a flaw has been fixed. Targets generally run the latest fully patched operating system available, unless a category specifies otherwise.
Sonos and AI tools also breached
McCaulay Hudson combined an out-of-bounds write and a format-string vulnerability against the Sonos Era 300, earning $50,000 and five points. VinSOC’s linhlhq and Son Dinh earned $17,500 and 3.5 points for a two-bug Sonos chain containing one publicly known flaw.
Xint’s Taisic Yun obtained a reverse shell on LiteLLM through improper input validation and code injection, earning $40,000 and four points. Out of Bounds researchers HaeJung Yang and ByungYoung Yi used four bugs against LiteLLM, two previously known, earning $15,000 and three points.
Other confirmed wins included VinSOC’s seven-zero-day Philips Hue Bridge Pro exploit, worth $40,000, and Team Confused’s single use-after-free against the Lexmark CX532adwe printer, worth $20,000.
Successful entrants must provide detailed exploit documentation, and the vulnerabilities are disclosed to affected vendors. Users and administrators should watch for subsequent security advisories and apply relevant updates when fixes become available.


Leave a Reply