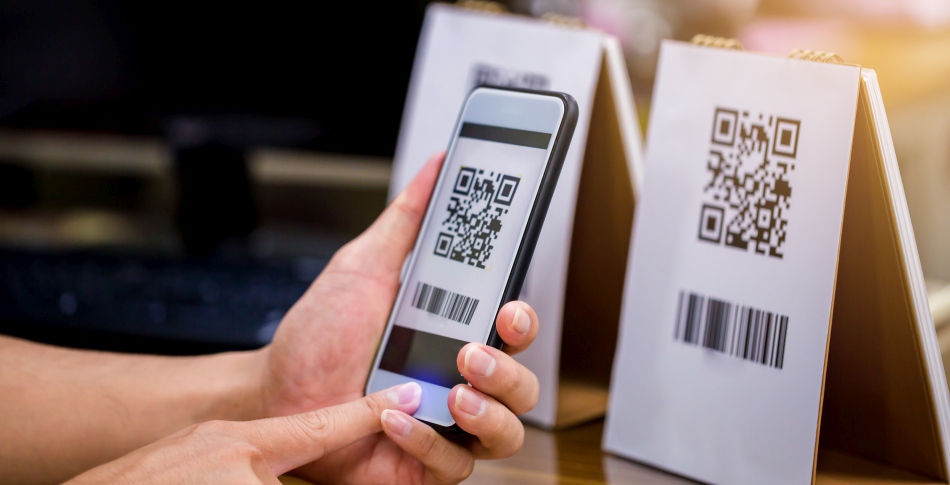
Abandoned branded QR code domains can be claimed through a weakness in QR Tiger’s custom domain feature.
The technique can send people scanning genuine, previously printed codes to an attacker’s website while their phones initially display the company’s legitimate domain.
Security researcher Farzan Karimi, who calls the technique “QR Jacking,” published his findings after scanning corporate domains and demonstrating a takeover using a real company’s physical QR code. He says he found hundreds of exposed subdomains across manufacturing, healthcare, financial services, and technology, but did not publicly identify the affected companies.
QR Tiger is a QR code management service that lets businesses replace their standard short links with addresses on their own domains. Through its “Own Short Domain” feature, a company can point a subdomain such as qr.company.com at QR Tiger and use it in QR campaigns.
How QR Jacking works
According to Karimi, QR Tiger accepts a custom domain after checking that its DNS record points to the platform. It does not require the person adding the domain to prove that they control it through a separate challenge.
That becomes a problem if a business stops using the service but leaves the DNS record in place. If the subdomain is no longer claimed within QR Tiger, someone with a different QR Tiger account can register it and direct traffic to a site they control, Karimi found. The attacker needs neither access to the company’s DNS settings nor access to its systems.
The risk extends to codes already printed on packaging, signs, or other materials. Karimi confirmed that a code from an old campaign could remain vulnerable if its branded domain still points to QR Tiger after the company abandons the integration. A scan would show the familiar corporate address before redirecting the visitor to the attacker’s chosen destination.
Karimi demonstrated the technique with a page under his control. A malicious operator could instead use a lookalike login page to seek credentials or other personal information.
No fix available, caution recommended
The researcher says he disclosed the issue to QR Tiger, but it remained unremediated five months later. He also says he has found similar ownership checks at other QR services and is disclosing those findings separately.
Organizations using branded QR links should review DNS records pointing to QR platforms and remove records for integrations they no longer control or use. QR service providers can address the underlying claim process by requiring independent proof of domain ownership, such as a unique DNS TXT record, before assigning a custom domain to an account.
People scanning a QR code should check the destination after the page loads, especially before entering a password or payment details. If a code unexpectedly leads to a login or payment page, visit the company’s website or app directly instead.


Leave a Reply