French mailing services provider Maileva confirmed that attackers stole the names and postal addresses of 22 million people in a September cyberattack.
Several thousand customer organizations were affected, and some have warned that the attackers may also have accessed information inside their letters.
Maileva confirmed the theft in writing to French media and also published a warning on its website yesterday. Internal records attributed to Docaposte listed roughly 39 million mailing references. Once duplicate recipients were removed, the total came to about 22 million people.
Maileva is part of Docaposte, a subsidiary of France’s La Poste group. Businesses and public institutions use the service to print and send invoices, payment reminders, and administrative documents. The people in the breach count are recipients of that correspondence, many of whom may have had no direct dealings with Maileva.
La Poste dates the attack to mid-September. Cyberattaque.org reported that Maileva suspended its services on September 23 after detecting suspicious activity. An early customer notice described attempts to access customer accounts and send unauthorized letters. Services were fully restored on September 29.
Maileva
Healthcare dates and billing details exposed
The confirmed tally covers recipients’ names and postal addresses. Customer notices describe additional exposure that varies by sender and by the documents involved.
Hôpital Foch in Suresnes told patients that an attacker may have viewed payment reminders sent between September 9 and 23. Those letters included invoice numbers, dates of care, and amounts owed. The hospital uses medical billing provider Kiwee.care, which in turn uses Maileva to print and mail reminders. Kiwee.care told Cyberattaque.org that the breach also affected correspondence it handled for other healthcare clients.
Social housing provider Flandre Opale Habitat warned that data from letters sent over the past decade could have been exposed, including tenant account numbers, housing details, and invoice amounts.
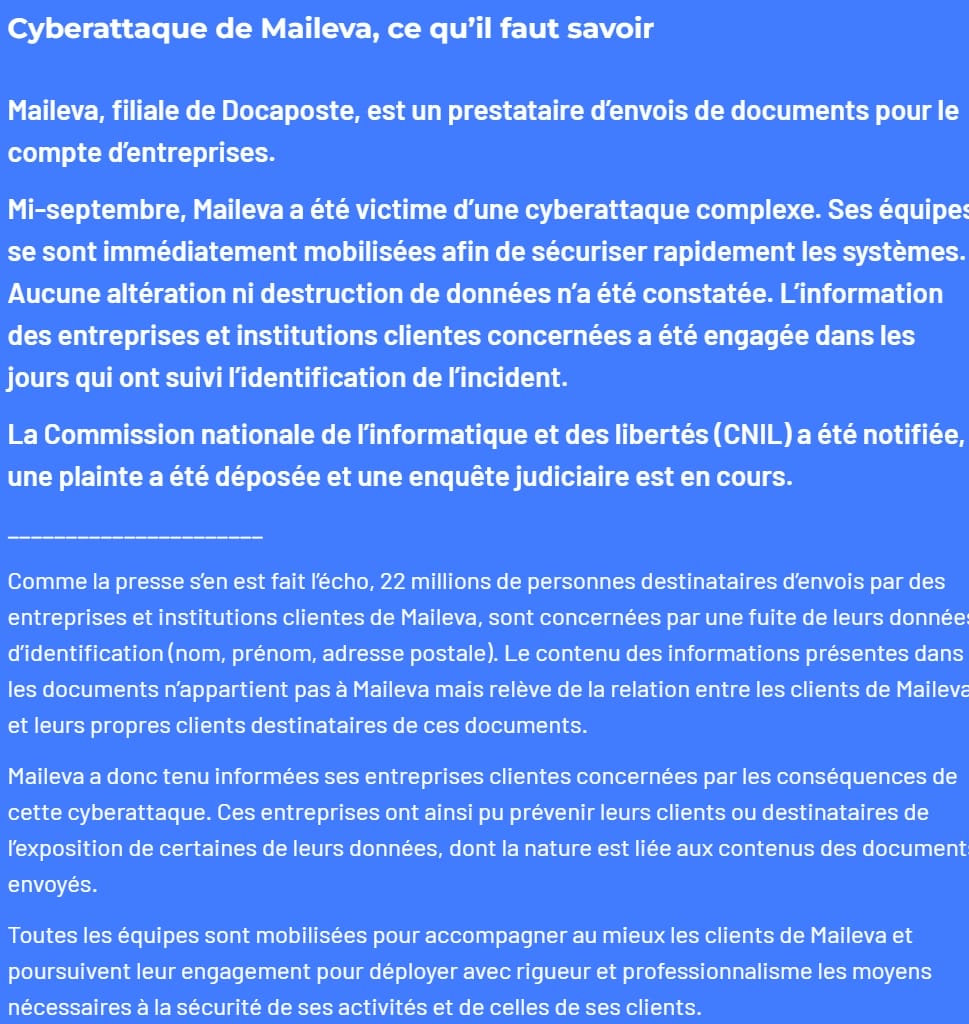
Maileva says it informed all affected organizations, which are responsible for contacting their own customers or other recipients. How many of the 22 million people have been notified remains unclear. Maileva reported the breach to France’s data protection authority, the CNIL, and filed a complaint. A judicial investigation is underway.
Potentially exposed individuals receiving an unexpected payment reminder should verify the amount and payment instructions directly with the sender using a phone number from its official website or customer portal.


Leave a Reply