CenterPoint Energy has confirmed that an unauthorized third party obtained personal information belonging to some of its customers through an external-facing system.
The disclosure follows an online post in which a threat actor claimed to have stolen and released information on approximately 7.49 million customers. However, CenterPoint has not confirmed that figure or the authenticity of the published dataset.
In a Form 8-K filed with the US Securities and Exchange Commission on September 14, 2026, CenterPoint said it became aware in September of a third-party post claiming to possess customer information. The utility activated its cybersecurity incident response procedures, brought in external cybersecurity specialists, and implemented additional measures to protect its systems.
The investigation subsequently determined that an unauthorized party had obtained personal information associated with “a portion” of CenterPoint customers through one of the company's externally accessible systems. CenterPoint has not disclosed how the system was compromised, how long it was exposed, or precisely what information was accessed.
CenterPoint Energy is a Houston-based electric and natural gas utility whose operations include CenterPoint Energy Houston Electric and CenterPoint Energy Resources. Its shares trade on the New York Stock Exchange under the ticker CNP. The company said the incident did not affect electricity and gas delivery, which remained operational.
The SEC filing appears to correspond with a forum post attributed to a threat actor using the alias “4d722e4d656f77.” The poster claimed to have obtained more than 7.49 million CenterPoint records from an API controlled by the company and alleged that the endpoint lacked adequate authentication, rate limiting, and other protections.
The post says the stolen data included fields such as customer names, phone numbers, email addresses, service and billing addresses, account and premise identifiers, billing amounts, payment information, autopay and paperless billing status, and the last four digits of Social Security numbers. The actor also claimed that substantially more data could have been extracted before CenterPoint intervened.
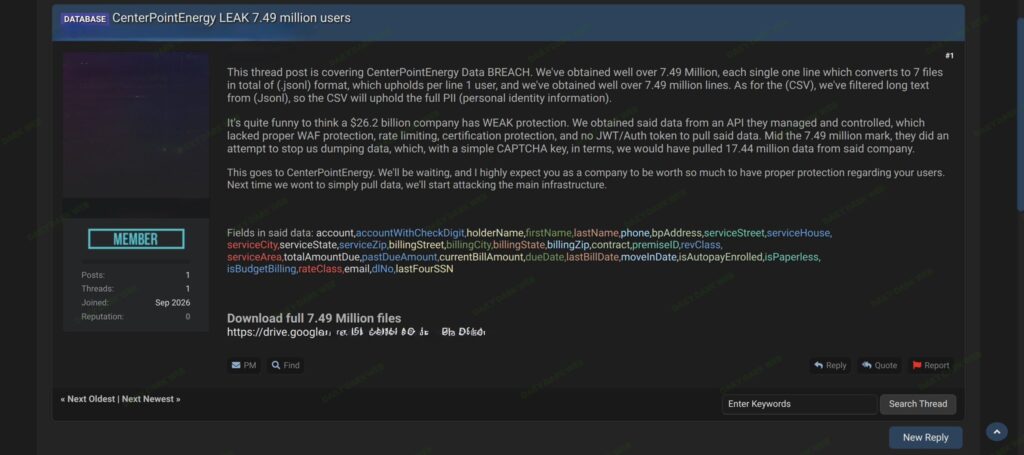
Those technical details and the claimed record count remain allegations by the threat actor and were not verified in CenterPoint's 8-K. The company has only confirmed unauthorized access to personal information through an external-facing system and said its investigation is still determining which customers and data types were affected.
CenterPoint has notified law enforcement and certain regulators and says it will notify affected customers and additional authorities where required. It expects to incur incident-response expenses but believes its cybersecurity insurance will offset some of those costs. The company currently does not expect the breach to materially affect its financial condition or operating results.
Customers should treat unexpected calls, emails, or text messages claiming to be from CenterPoint with caution, particularly when they reference account balances or service information. Affected individuals should monitor financial accounts and credit reports, consider placing a credit freeze, and independently contact CenterPoint through official channels rather than using links or phone numbers supplied in unsolicited messages.


Leave a Reply