ASOS customers reported receiving an alarming push notification on October 6 claiming that the online fashion retailer’s Snowflake instance had been compromised and threatening to leak data.
The alleged breach remains unconfirmed, with the message offering no details about what information may have been accessed.
Reports emerged on Reddit and X on Tuesday morning as shoppers shared screenshots and questioned whether the alert was legitimate. A user said their partner had received the notification in the UK, while two commenters reported receiving the same message in the United States.
CyberInsider
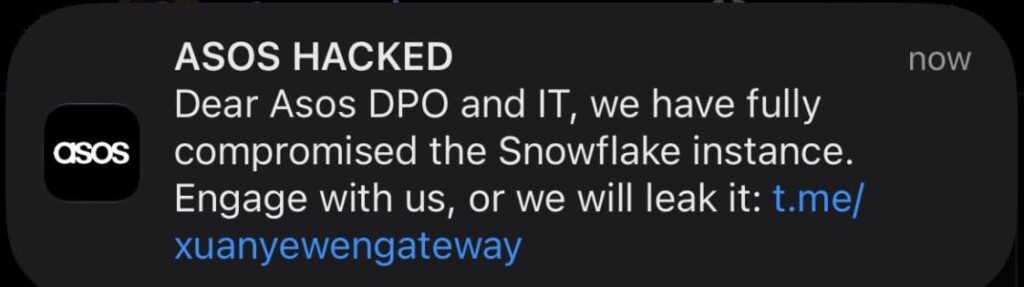
The screenshot supplied to CyberInsider through a tipster shows a notification bearing the ASOS app icon and the heading “ASOS HACKED.” Its text addresses the retailer’s data protection officer and IT team directly:
“Dear ASOS DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it.”
ASOS is a UK-based online fashion retailer selling its own labels and products from hundreds of partner brands. According to its corporate website, it serves approximately 17 million customers across more than 150 markets each year. That figure describes its overall customer base, not the number of people who received the notification or may be affected by any breach.
The message ends with a Telegram link, apparently intended as a contact channel for the company. It does not identify the sender, specify a ransom amount, describe the allegedly compromised data, or provide evidence of data theft.
On X, several users separately reported receiving the alert. However, the total number of recipients remains unknown.
Snowflake provides a cloud platform that organizations use to store, process, and analyze data. The notification’s wording refers to an alleged compromise of ASOS’s environment on that platform, but it does not establish that Snowflake’s own infrastructure was breached.
Taken together, the reports suggest an unauthorized message was distributed through a channel associated with the ASOS app. However, they do not establish how it was sent, whether a third-party service was involved, or whether the sender actually accessed a Snowflake account.
ASOS had not publicly confirmed the alleged breach at the time of writing, and the retailer did not immediately respond to our request for comment.
Customers should avoid following the Telegram link or engaging with whoever posted the message. For updates, they should visit ASOS’s website directly and be cautious of follow-up messages asking for passwords, payment information, or money related to the incident.


Leave a Reply