The ShinyHunters cybercrime group is now claiming it breached FBI systems after discovering and immediately exploiting a previously unknown vulnerability in Oracle PeopleSoft.
This allegedly gave them access to several internal services and allowed them to steal between 2TB and 3TB of data.
The FBI has not yet confirmed the intrusion, and CyberInsider has contacted the agency for comment but has not received a response at the time of publication.
ShinyHunters told CyberInsider that it discovered the PeopleSoft vulnerability on Monday night and used it against the FBI shortly afterward. The group says the vulnerability remains a zero-day, with details of the flaw not publicly disclosed.
According to the threat actor, exploiting the vulnerability provided remote code execution (RCE) on an FBI server. ShinyHunters claims it then moved laterally into other FBI-managed infrastructure, including systems hosted in AWS GovCloud, before downloading large quantities of data.
The group named three allegedly compromised services, “Criminal Justice (CJ),” “Human Resources (HR),” and “Medlink,” and said it was still reviewing the stolen material to determine what other systems and information had been accessed.
One screenshot shared with CyberInsider shows a page on apply.fbijobs.gov under a /PSEMHUB/ path that appears to display Linux system information. ShinyHunters described this system as its entry point into the FBI environment.
The particular domain is part of the FBI's employment and recruitment infrastructure. Oracle PeopleSoft is an enterprise software suite commonly used by organizations for human resources, recruiting, payroll, and other administrative functions.
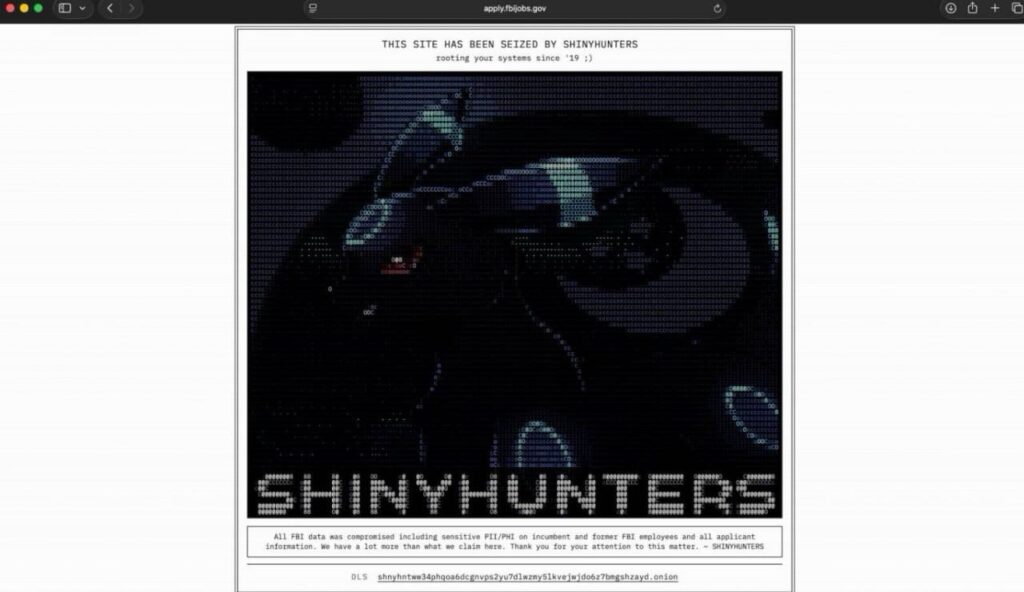
ShinyHunters also provided a screenshot showing the FBI Jobs portal apparently defaced with a message claiming the site had been “seized by ShinyHunters.” The group says the defacement was visible only briefly before the FBI noticed it and took the service offline.
CyberInsider
The defacement message claims that information belonging to FBI employees, former employees, and applicants was compromised, including personally identifiable information (PII) and protected health information (PHI). CyberInsider has not independently verified the contents or volume of the allegedly stolen data.
ShinyHunters said the FBI became aware of the incident on Tuesday and subsequently displayed a “Scheduled maintenance underway” message.
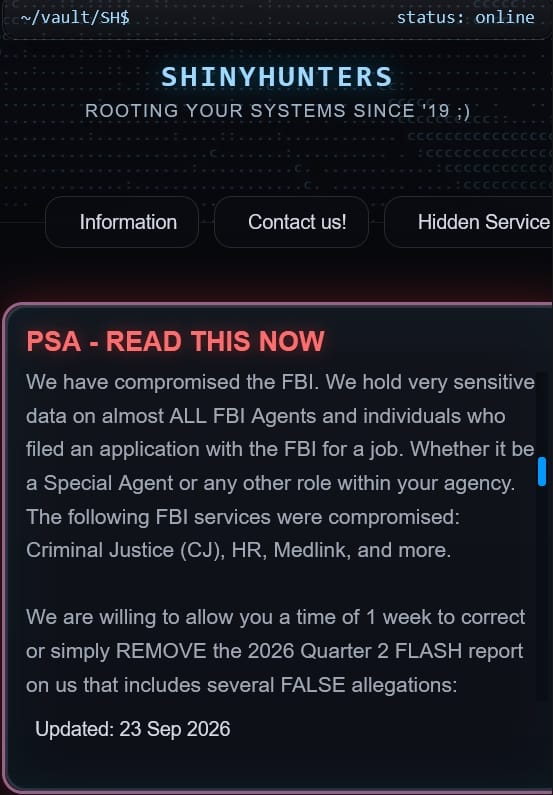
The threat actor also published a new entry on its extortion site demanding that the FBI removes the recent PSA it published on them, which allegedly contains false information. The threat actor gave the law enforcement agency one week to take action, or they threaten to leak the stolen data online.
ShinyHunters has leveraged Oracle PeopleSoft vulnerabilities again recently, to target organizations in the education sector. The threat actor told CyberInsider that they plan to exploit this newest zero-day against a broader spectrum of targets.
This is a developing story. CyberInsider will update this report if the FBI provides a statement, Oracle confirms the claimed PeopleSoft zero-day flaw, or additional evidence about the attack becomes available.


Leave a Reply