A browser extension installed by more than 30,000 Twitch users was found forwarding live OAuth session tokens to proxy servers operated by Russian-language bot service JeetBot.
The tokens could let anyone who possesses them act on affected Twitch accounts without the account password or two-factor authentication.
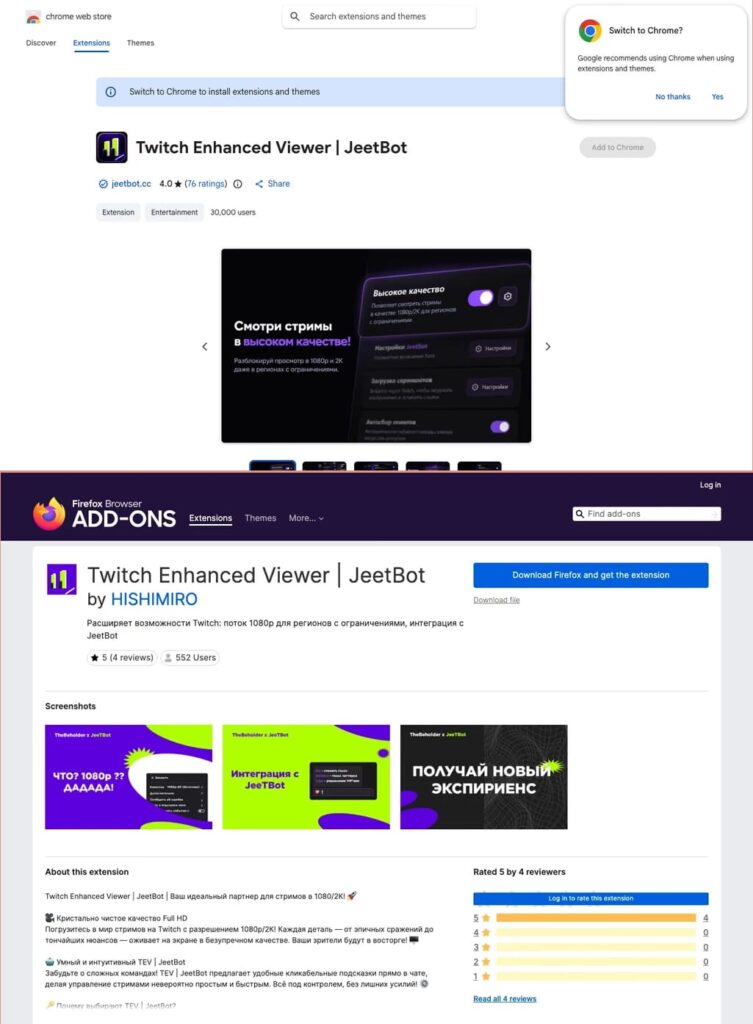
Socket Threat Research Team disclosed the findings after analyzing the Chrome and Firefox versions of “Twitch Enhanced Viewer | JeetBot.” The extension remains listed under Chrome ID pnhhdhhcadcjfckjhpmjneldiegbojfb, with roughly 30,000 users, while its Firefox version reportedly has another 552 installations.
Socket
The extension advertises features including Twitch ad blocking, forced 1080p playback, regional stream unlocking, and automatic channel-point collection. To provide some of these functions, it redirects Twitch video-playlist requests through infrastructure controlled by the extension operator.
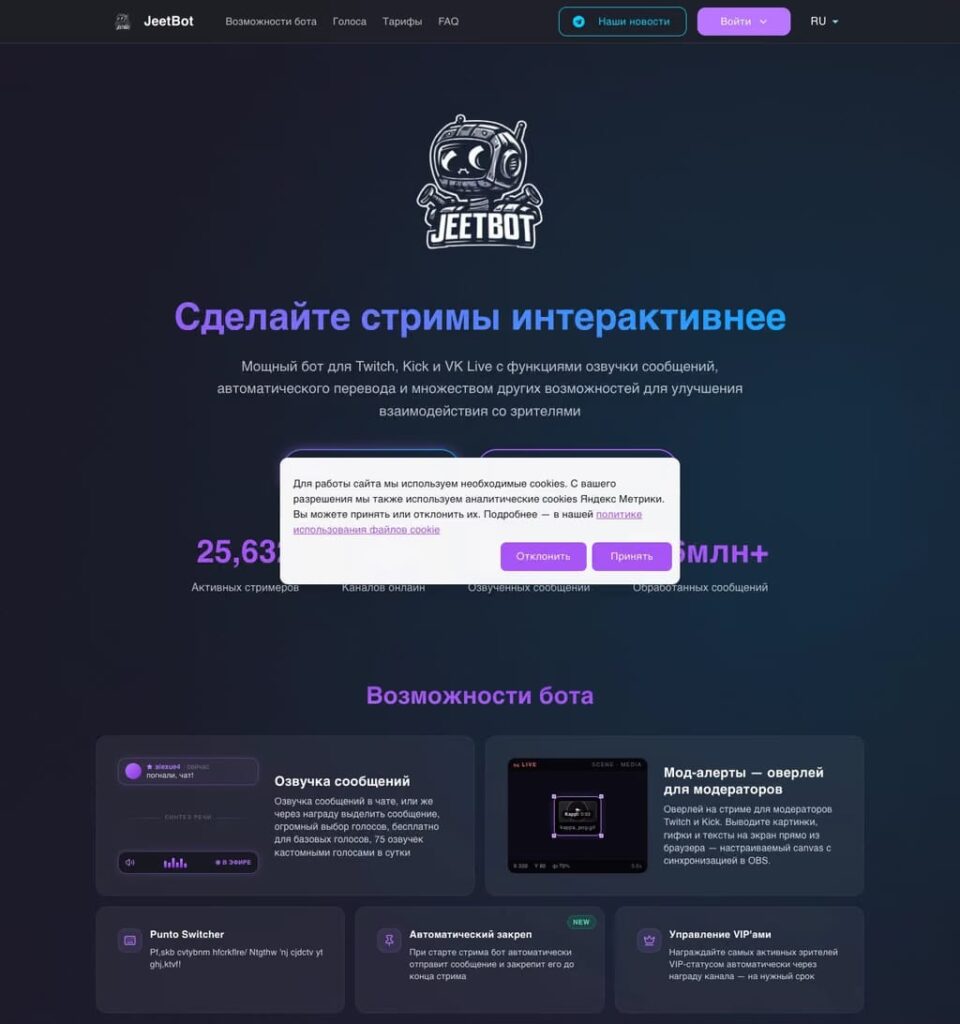
JeetBot is a commercial Russian-language service offering automation and botting functionality for Twitch, Kick, and VK-Live.
Socket
According to Socket’s code analysis, the extension’s content script captures the Authorization header used by Twitch’s own web client and sends it to the background worker. The worker extracts the OAuth token and, in current 85.x releases, appends it to proxied playlist requests as an auth URL parameter.
The default destination is enhanced[.]jeetbot[.]cc, while additional proxy and configuration infrastructure includes ext-styles[.]jeetbot[.]cc and proxy[.]morphilina[.]me.
Placing the token in a query string also means it can be recorded in ordinary proxy request logs. Socket determined that the credential is an account-scoped Twitch OAuth token rather than a limited video-playback token. Such credentials can potentially be used to send or read whispers, participate in chat, change account-related settings, and spend channel points.
The extension excludes ten hardcoded Russian-language streamer channels from token forwarding. For other channels, the token is passed to the operator-controlled proxy.
Earlier 4.x versions were more explicit. Version 4.8, released in January 2026, POSTed captured tokens to a /set-token endpoint hosted on JeetBot infrastructure, with backup endpoints at deno.dev and deno.net. The code also tracked previously sent tokens and applied a five-second cooldown, suggesting tokens were intentionally collected server-side.
Socket noted that the behavior conflicts with the extension’s disclosures, including claims that it does not collect, store, or process user data.
Users who installed Twitch Enhanced Viewer | JeetBot should remove the extension and invalidate existing Twitch sessions by signing out of all devices, then signing back in.


Leave a Reply